AI Transformation Is a Problem of Governance — Because Scaling AI Changes Who Makes Decisions
The hardest part of enterprise AI is no longer getting a model to work; it is deciding what that model is allowed to do, who owns the consequences, and when a human must intervene.

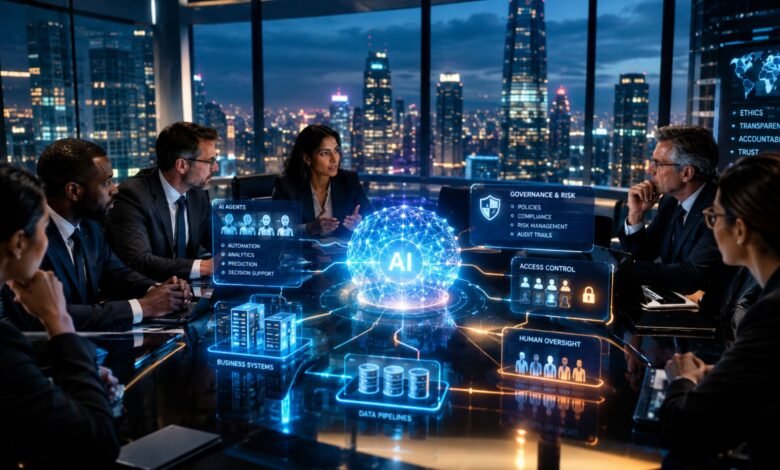
Artificial intelligence has moved beyond the experimental corner of the IT department. In 2026, organisations are embedding AI into customer service, software development, finance, procurement, marketing, operations, analytics and public services. The technology is becoming easier to deploy at exactly the moment its decisions are becoming harder to contain.
That creates a less glamorous but more consequential question: who is actually in charge?
An employee can install an AI assistant in minutes. A business can connect an agent to internal systems in days. But once that system can access confidential information, recommend consequential decisions or execute actions through APIs, the problem changes from software selection to organisational control.
The governance question is therefore no longer theoretical. Deloitte’s 2026 research, based on 3,235 business and technology leaders across 24 countries, found that only 21% of respondents said their organisation had mature governance for agentic AI, even as adoption is expected to increase sharply.
AI transformation is a governance problem because AI changes decision rights, data access, accountability, risk exposure and operating processes at the same time. Technology can provide the capability, but governance determines who may deploy it, what it can access, which decisions it can make, how its outputs are checked, and who remains accountable when something goes wrong.
The real transformation begins when AI stops being a tool
There is a major difference between using AI and transforming a business with AI.
Using AI might mean asking an employee assistant to summarise a report, generate marketing copy or draft software documentation. Transformation happens when the organisation changes the underlying workflow because AI is now part of how work is performed.
That distinction is visible in McKinsey’s 2025 global survey. More than three-quarters of respondents said their organisations used AI in at least one business function, yet only 21% of respondents reporting generative-AI use said their organisations had fundamentally redesigned at least some workflows. The same research found that 28% said the CEO was responsible for AI governance and 17% said AI governance was overseen by the board.
The numbers reveal the organisational gap.
AI adoption can spread horizontally without changing the company’s power structure. AI transformation cannot.
Once AI enters a core process, somebody has to decide:
- Which AI systems are approved?
- Who owns the business outcome?
- What data may a model access?
- What decisions can be automated?
- What decisions require human review?
- Who can switch an AI system off?
- What happens after a model changes?
- How is an error reported?
- Which executive accepts the residual risk?
- How is value measured after deployment?
Those are governance decisions, not model-selection decisions.
A useful distinction: governance is the control system, not the transformation itself
There is a temptation to describe every AI failure as a governance failure. That goes too far.
Governance can establish rules, decision rights and risk controls, but it does not automatically redesign a broken workflow, teach employees how to work differently or create a viable business case.
Scaled Agile makes this distinction explicitly, arguing that governance is a necessary starting point but that organisational structure, leadership alignment, workforce readiness and execution determine whether AI can actually scale.
BCG’s research reaches a similar conclusion from another direction. Its 2026 work argues that AI-driven transformation is heavily dependent on people and organisational change, with its frequently cited 10/20/70 framework assigning roughly 10% of effort to algorithms, 20% to technology and data, and 70% to people and processes.
That leads to a more precise formulation:
AI transformation is not governance instead of technology. It is technology operating inside a governance and organisational system.
The distinction matters because excessive governance can produce another failure mode: everything is controlled, nothing is scaled.
A company can create a 40-page AI policy and still have no practical answer to which systems are running, which employees have access to them, or who is accountable for an autonomous action.
The governance gap becomes dangerous when AI starts acting
Generative AI created governance problems around accuracy, intellectual property, privacy and data handling.
Agentic AI adds another dimension: action.
A chatbot can produce a wrong answer. An agent connected to business systems may produce a wrong answer and then act on it.
Deloitte’s 2026 research describes the resulting gap directly. Only 21% of surveyed organisations reported mature governance for agentic AI, while roughly 80% lacked mature capabilities such as clear boundaries on autonomous decisions, real-time monitoring and audit trails.
That changes the minimum requirements for responsible deployment.
| AI capability | Governance question |
|---|---|
| Generate text or code | What can be generated and where may it be used? |
| Retrieve internal data | Which users, systems and datasets may it access? |
| Recommend a decision | Who reviews the recommendation? |
| Trigger an API | What actions can it execute independently? |
| Operate continuously | Who monitors it after deployment? |
| Change behaviour after updates | Who evaluates and approves the change? |
| Use third-party models | Who owns supplier and model risk? |
| Make high-impact decisions | Where is mandatory human oversight required? |
This is why AI governance should not be treated as a static policy document.
It needs to operate as a control layer around actual systems.
NIST’s AI Risk Management Framework provides a useful operational model through four functions: Govern, Map, Measure and Manage. Its guidance is designed to help organisations incorporate trustworthiness considerations across the lifecycle of AI systems rather than treating risk assessment as a one-time event.
The AI inventory may become the most boring document in the company — and one of the most valuable
Many companies know what software they purchased.
Fewer know exactly where AI is being used.
That distinction becomes increasingly significant as employees select consumer AI services independently, departments procure specialised tools, developers connect APIs and agents begin operating across multiple systems.
An organisation cannot govern what it cannot identify.
The first practical control is therefore an AI inventory containing, at minimum:
- AI system or model name
- Business owner
- Technical owner
- Purpose and business process
- Data accessed
- Third-party providers
- User groups
- Risk classification
- Level of autonomy
- Human approval requirements
- Evaluation method
- Monitoring arrangements
- Incident contacts
- Change and version history
- Retirement or shutdown procedure
NIST’s Generative AI Profile specifically identifies governance, third-party considerations, human review, tracking, documentation, change-management controls and data provenance as relevant governance mechanisms for generative AI.
This is also where AI transformation begins to resemble other mature corporate disciplines.
Cybersecurity teams maintain asset inventories.
Finance teams maintain accounting controls.
Quality teams maintain production procedures.
AI needs equivalent organisational memory.
Without it, the company discovers its AI architecture only after an incident, an audit, a customer complaint or a regulator’s request.
Boardroom governance is about decisions, not technical ownership
One of the most persistent mistakes is assigning AI exclusively to the chief technology officer or chief information officer.
Technology leaders should obviously own substantial portions of implementation. But AI transformation also affects risk, finance, legal, HR, operations, procurement, customer relationships and corporate strategy.
McKinsey’s 2025 survey found that AI governance is often jointly owned, with respondents reporting an average of two leaders responsible for it. It also found that CEO oversight of AI governance was associated with higher self-reported bottom-line impact, although the study describes a correlation rather than proving causation.
That caveat matters.
Governance should not become another executive title attached to AI. The key question is whether decision rights are actually clear.
A mature model might divide responsibilities roughly like this:
| Governance layer | Core responsibility |
|---|---|
| Board | Strategic risk appetite, major exposure and oversight |
| CEO / executive leadership | Enterprise priorities, value targets and accountability |
| CIO / CTO | Architecture, technical controls and deployment |
| Chief Risk / Compliance / Legal | Regulatory, legal and risk requirements |
| CISO | Security, access and threat controls |
| Data leadership | Data quality, provenance and access |
| Business owner | Operational performance and final business accountability |
| AI governance function | Policy, inventory, standards, reporting and coordination |
| Employees | Approved use, escalation and responsible human review |
The exact structure will vary by organisation.
The principle does not.
The person who owns the business outcome cannot be replaced by the person who owns the model.
An AI system can make a recommendation. A model provider can supply the infrastructure. A technology team can maintain the integration. None of those facts automatically transfer accountability for the business decision.
Governance becomes real when it reaches the API layer
An AI policy that exists only in a PDF is weak governance.
Operational governance appears inside the technical architecture.
Consider an AI agent authorised to process customer refunds. A practical control system could require:
- identity verification;
- a restricted data-access scope;
- pre-approved transaction limits;
- retrieval only from approved sources;
- policy checks before an action;
- human approval above a defined threshold;
- complete logging of the agent’s steps;
- automated alerts for anomalous behaviour;
- post-action reconciliation;
- a mechanism to disable the agent immediately.
That architecture converts an abstract principle — “use AI responsibly” — into enforceable behaviour.
The same logic applies to coding agents, procurement agents, financial analysis tools, HR systems and customer-facing assistants.
The broader engineering lesson is simple:
The model is only one component. The control environment determines what the model can actually do.
This is increasingly relevant to businesses building connected automation systems, where AI agents are combined with permissions, human approval checkpoints, monitoring and audit-ready logs. GlobalNova’s recent examination of the AI-first software agency Enntal provides a useful example of that broader systems approach. GlobalNova: Enntal and the AI-first software agency model
ISO/IEC 42001 turns AI governance into a management-system discipline
Governance becomes considerably more tangible when it moves from principles to management systems.
ISO/IEC 42001:2023 specifies requirements for establishing, implementing, maintaining and continually improving an Artificial Intelligence Management System. ISO describes it as applicable to organisations that develop, provide or use AI-based products and services across sectors.
That matters because it changes the mindset.
Instead of asking:
“Do we have an AI policy?”
the organisation begins asking:
“What system do we use to identify AI risks, assign responsibilities, assess controls, monitor performance and improve the programme?”
ISO/IEC 42001 addresses areas including leadership, planning, AI policy, risk management, data governance, transparency, performance evaluation and continual improvement. Certification is voluntary and is conducted by independent certification bodies rather than ISO itself.
For organisations managing large AI estates, that kind of structure can make governance auditable rather than aspirational.
It also makes AI governance compatible with existing management disciplines such as information security and enterprise risk management.
Regulation is forcing governance out of the policy drawer
The European Union provides one of the clearest examples of governance moving into operational requirements.
As of 2 August 2026, enforcement powers for significant portions of the EU AI Act are active, including rules concerning prohibited AI practices, certain transparency obligations and general-purpose AI models. Certain transparency provisions apply from that date, while particular high-risk obligations are scheduled for later dates.
The European Commission’s current guidance also addresses AI systems that interact with people or generate content, including transparency requirements under Article 50. The Commission states that these obligations apply from 2 August 2026, with a limited grace period for some systems already on the market regarding marking and detection of AI-generated content.
This matters to enterprise governance because regulation rarely stops at the model.
It reaches the organisation around the model.
Questions suddenly become practical:
Who is the provider?
Who is the deployer?
What system is being used?
What data enters it?
What documentation exists?
What transparency information is available?
What monitoring is being performed?
Who can demonstrate compliance?
Governance is the machinery that answers those questions.
Governments are discovering the same organisational problem
The problem is not confined to private companies.
The OECD’s Digital Government Outlook 2026 reports that AI is now used in at least one area of government in 35 of 36 OECD countries, or 97%. It also reports that 30 of 36 countries — 83% — have at least one institution responsible for governing AI in the public sector.
Yet the OECD identifies uneven conditions for scaling AI, including data governance, skills, infrastructure, procurement and organisational capacity. It also notes that oversight frequently focuses more on guidance than enforcement and that weak impact measurement can contribute to a proliferation of pilots that fail to scale.
That is remarkably close to the enterprise problem.
The technology is not necessarily the limiting factor.
Institutional capacity is.
The OECD’s 2025 report on government AI identified seven major enablers for effective adoption: governance, data, digital infrastructure, skills, investment, procurement and partnerships. Its later 2026 outlook again places strong governance at the centre while emphasising the need for strong foundations underneath it.
The message is broader than “write more rules”.
Governance needs the capacity to function.
What AI governance should actually control
A mature governance programme should answer five different questions across the AI lifecycle.
1. Is this AI use case allowed?
Not every technically possible application belongs in an organisation’s risk appetite.
The governance system should determine which use cases are prohibited, restricted, conditionally approved or low risk.
2. Is the data allowed?
Data governance is inseparable from AI governance.
Questions include ownership, consent where applicable, confidentiality, retention, provenance, access controls and whether information may be transmitted to an external model provider.
3. What can the system decide?
This is especially important for AI agents.
A system that drafts an email has a different risk profile from one that sends it. A system that recommends a payment has a different risk profile from one that executes the payment.
Autonomy should therefore be designed deliberately rather than inherited from a software integration.
4. How do we know it works?
NIST’s framework emphasises measurement and management across the lifecycle. Evaluation should address more than model accuracy; depending on context, it may include security, robustness, privacy, bias, reliability, explainability and real-world impact.
5. What happens when it fails?
Governance is incomplete without incident response.
An organisation needs to know who receives the alert, who investigates the issue, who can suspend the system, who communicates with affected stakeholders and how corrective action is recorded.
That is where accountability becomes observable.
The hidden economic problem: AI can create activity without creating value
The governance debate sometimes focuses so heavily on safety that it ignores another problem: value.
An organisation can deploy hundreds of AI tools and still fail to produce meaningful economic transformation.
McKinsey’s 2025 research found that 47% of respondents reported at least one negative consequence from generative AI, with inaccuracy, cybersecurity and intellectual-property infringement among commonly reported risks. Its research also found that workflow redesign had the strongest effect among the attributes tested on an organisation’s ability to see EBIT impact from generative AI.
McKinsey separately described what it called a “gen AI paradox”: widespread adoption alongside limited material impact, with many higher-value use cases remaining stuck in pilot mode.
The implication for governance is profound.
A governance committee should not only ask:
“Is this AI safe?”
It should also ask:
“Why are we using it?”
And then:
“What process changes because of it?”
And finally:
“What measurable outcome proves that the change worked?”
Without those questions, governance becomes a compliance exercise rather than a transformation discipline.
The strongest operating model may be neither centralised nor decentralised
Centralised governance provides consistency.
Decentralised teams provide speed.
AI transformation needs both.
McKinsey’s survey found that organisations often centralise risk and compliance as well as data governance, while using more hybrid structures for technical talent and adoption.
This suggests a practical model:
Centralise the rules. Distribute the execution.
The centre establishes:
- risk tiers;
- approved providers;
- data rules;
- minimum security controls;
- documentation requirements;
- evaluation standards;
- escalation paths.
Business teams then adapt those controls to individual workflows without having to request permission for every low-risk experiment.
That is the difference between governance as a brake and governance as infrastructure.
The AI transformation timeline is moving faster than the governance timeline
| Period | Enterprise AI development | Governance implication |
|---|---|---|
| 2023 | Generative AI becomes widely accessible | Shadow AI and data-use questions emerge |
| 2024 | Organisations formalise responsible-AI programmes | Risk management frameworks become operational priorities |
| 2025 | AI spreads across business functions | Workflow redesign and executive ownership become more important |
| 2026 | Agentic AI receives greater attention | Permissioning, monitoring and auditability become central |
| 2026 onward | Regulatory obligations expand | Governance must connect policy to evidence and controls |
NIST’s AI RMF and Generative AI Profile provide risk-management structures, while ISO/IEC 42001 provides a management-system approach. The EU AI Act adds legally binding requirements within its jurisdiction, with provisions becoming applicable on a phased timetable.
The pattern is clear enough to state without exaggeration:
The further AI moves into core operations, the less useful governance becomes as a document and the more necessary it becomes as a living operating system.
Six signals that an AI programme has a governance problem
Nobody can produce a complete AI inventory
Unknown systems are effectively ungoverned systems.
Different departments use contradictory rules
One business unit permits customer data in a tool that another has prohibited.
No one can identify the final accountable owner
Everyone can explain who built the model, but nobody can explain who owns the business outcome.
Agents have permissions broader than their job requires
Excessive privileges convert model mistakes into operational incidents.
Monitoring stops at deployment
A model may perform well in testing while behaving differently in production because users, data, prompts, integrations and surrounding systems change.
The organisation measures usage instead of outcomes
Counting prompts, users or AI-generated documents says little about whether the business actually improved.
These are not merely IT problems.
They are failures in organisational design.
A practical AI governance blueprint for the next stage
A company starting from scratch does not need a giant bureaucracy.
It needs clear sequencing.
Establish ownership before expanding deployment
Assign executive sponsorship and identifiable business owners for material AI systems.
Build one AI register
Create a single inventory covering internally developed systems, third-party software, APIs, copilots and agents.
Classify use cases by risk
Do not treat a marketing-writing assistant and an autonomous financial workflow as equivalent.
Define decision boundaries
For each system, specify what it may recommend, what it may execute and what requires human approval.
Restrict data and permissions
Apply least-privilege access to AI systems just as organisations do with other digital systems.
Introduce evaluation before production
Test representative data, edge cases, unacceptable outputs, security threats and failure scenarios.
Log actions, not merely answers
For autonomous systems, the organisation may need to reconstruct what the agent saw, decided and did.
Establish shutdown procedures
Every consequential AI system should have a known mechanism for suspension, rollback or containment.
Measure business outcomes
Set KPIs around revenue, cost, throughput, quality, customer outcomes, risk reduction or another meaningful business measure.
Review governance as systems change
AI governance cannot be “completed”. New models, providers, regulations, integrations and capabilities change the risk profile.
NIST’s lifecycle-oriented approach, ISO/IEC 42001’s continual-improvement model and OECD’s emphasis on ongoing governance all point toward this recurring rather than one-off approach.
The question leaders should ask before buying another AI system
The most revealing AI governance question is not:
“Which model is the most powerful?”
It is:
“What organisational decision are we changing, and who remains accountable for it?”
That question forces the technology conversation into business reality.
It exposes unnecessary pilots.
It highlights weak processes.
It reveals missing data.
It identifies unclear authority.
It makes risk explicit.
And it creates a much stronger connection between AI spending and measurable outcomes.
BCG’s 2026 work on AI transformation repeatedly places people, processes, leadership and organisational alignment at the centre of value creation, while McKinsey’s research similarly links workflow redesign and senior governance with stronger reported outcomes.
People Also Ask About AI Transformation and Governance
What does “AI transformation is a problem of governance” mean?
AI transformation is a governance problem because introducing AI changes who can make decisions, access information, execute actions and accept risk. Governance defines decision rights, accountability, permissible data use, human oversight, monitoring and escalation. It does not replace process redesign or workforce change, but it provides the operating controls within which those transformations can happen responsibly.
Why does AI transformation fail without governance?
AI transformation can fail without governance because departments may adopt disconnected tools, use inconsistent data policies, duplicate investment, create unclear accountability and give AI systems excessive permissions. Agentic AI increases the exposure because systems can move from generating recommendations to taking actions. Deloitte’s 2026 research found only 21% of surveyed organisations reported mature governance for agentic AI.
Is AI governance the same as AI compliance?
AI governance is broader than compliance. AI governance covers internal decision rights, risk management, data access, system ownership, monitoring, performance, human oversight and organisational accountability. Compliance addresses applicable legal and regulatory requirements. Standards such as ISO/IEC 42001 can support governance, while laws such as the EU AI Act create binding obligations within their scope.
Who should own AI governance in a company?
AI governance usually requires shared ownership rather than a single department. Executive leadership establishes strategic accountability; technology teams handle architecture; security manages technical exposure; legal and compliance address regulatory requirements; data teams govern information; and business owners remain accountable for operational outcomes. McKinsey’s 2025 survey found that organisations commonly assign AI governance jointly to multiple leaders.
What is the NIST AI Risk Management Framework?
The NIST AI Risk Management Framework is a voluntary framework designed to help organisations manage AI risks and promote trustworthy and responsible AI. Its core operating functions are Govern, Map, Measure and Manage, covering risk governance, context and impact assessment, evaluation and ongoing risk treatment. NIST also provides a Generative AI Profile addressing additional risks and governance considerations.
Does AI governance slow innovation?
AI governance can slow innovation when controls require excessive approvals for low-risk work, but well-designed governance can also increase speed by establishing pre-approved tools, risk categories, data rules and deployment patterns. The objective is not maximum control; it is proportionate control. A useful governance model allows low-risk experimentation while applying stronger oversight to high-impact or autonomous systems.
Governance Is Becoming Part of the AI Product
The early AI conversation centred on models: parameters, benchmarks, capabilities and performance.
The enterprise conversation is shifting.
A production AI system now sits inside a network of permissions, workflows, data sources, policies, human decisions, monitoring systems and legal obligations. The model is only one component of that environment.
That is why “AI transformation is a problem of governance” is useful as a starting proposition — provided it is not interpreted as “governance alone solves transformation”.
It does not.
Transformation also requires redesigned processes, capable employees, reliable data, infrastructure, leadership alignment and a business case that survives contact with reality. BCG, McKinsey and the OECD all point to versions of that broader organisational challenge, while NIST and ISO provide frameworks for turning governance principles into repeatable operational controls.
The deeper shift is this: once AI gains the ability to influence or execute consequential work, governance is no longer an administrative layer placed around technology.
It becomes part of the technology itself.
The organisations that understand that distinction will not necessarily be the ones with the most AI tools. They will be the ones that can explain, system by system, why an AI capability exists, what authority it has, what evidence supports its use, and who remains responsible for its consequences.
Editorial Disclaimer
This article distinguishes documented research, regulatory information and professional analysis from editorial interpretation. AI governance requirements vary by jurisdiction, sector, system type and deployment context. Regulatory provisions can change, and organisations should consult the applicable legislation, standards, regulators and qualified professional advisers before relying on this article for compliance decisions.


4 Comments